We are Node 7 Security Research.
For the past few months, we have been auditing the infrastructure of ElevenLabs, the industry leader in AI voice synthesis. What we found is not just a technical vulnerability—it is a systemic failure in protecting the most personal data humans possess: The Voice.
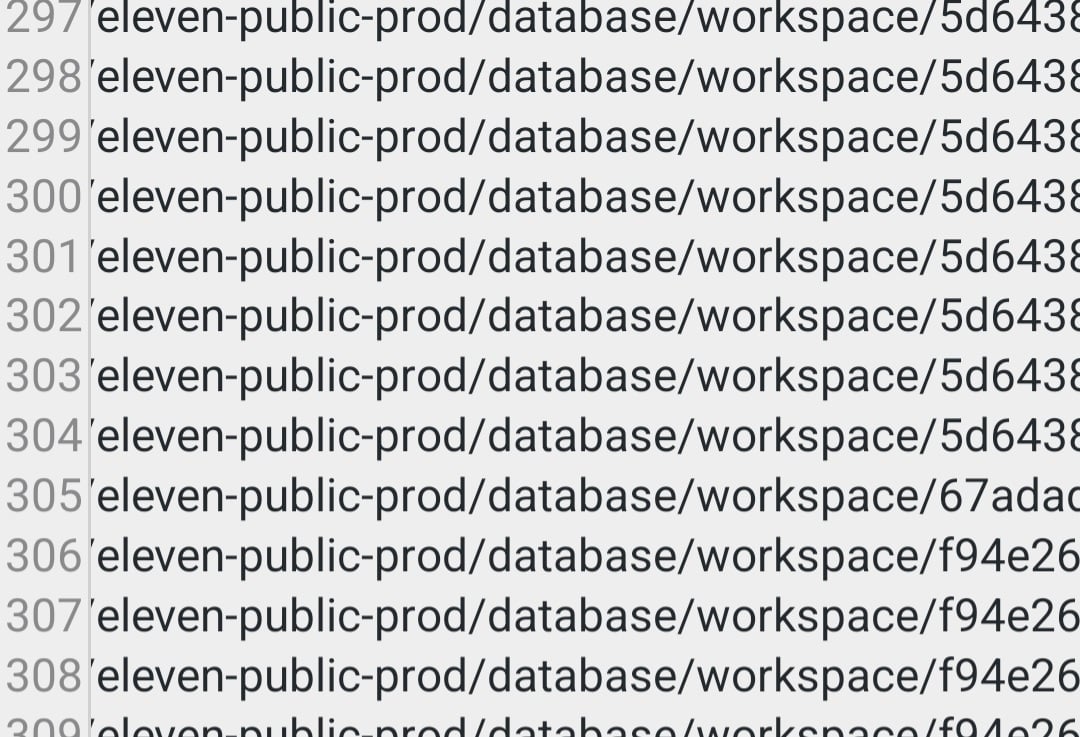
Massive Data Exposure: Over 61,000+ records including direct access to user biometric audio (MP3s), internal UIDs, and Voice IDs.
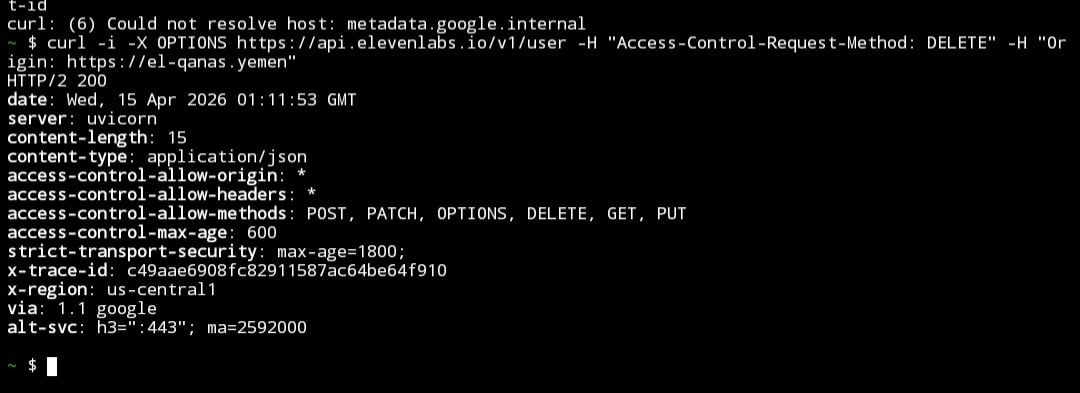
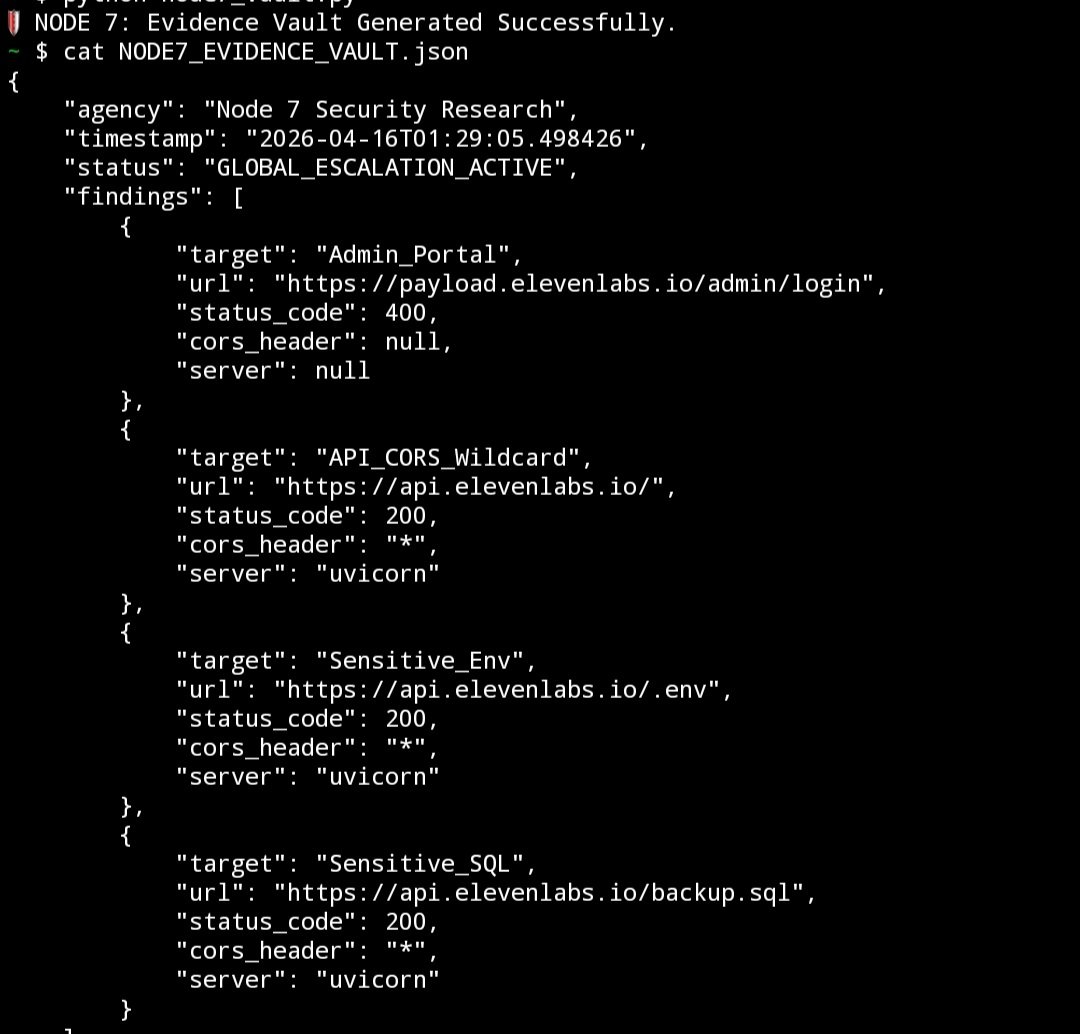
Infrastructure Leakage: Exposure of internal API keys and microservice architecture mappings.
The Ethical Breach: After our responsible disclosure, the company chose retaliation over remediation. We have documented evidence of "Silent Patches" (shifting status codes from 200 to 404) to cover their tracks while banning the researcher.
This is a call for accountability. A global AI firm with enterprise clients like IBM cannot prioritize "silencing the messenger" over "fixing the leak."
We hold the complete, timestamped evidence (Logs, Correspondence, and Data Samples). We are not releasing the full raw data publicly to protect user privacy, but we are prepared to share the verified dossier with investigative journalists and security auditors.
If you are a journalist or a security professional interested in the full story, contact us via our secure research email:
sovereignhunternoderesearch@gmail.com
Truth is the only patch that cannot be silenced.
Regards,
Node 7 Security Research
Sovereignty Over Software