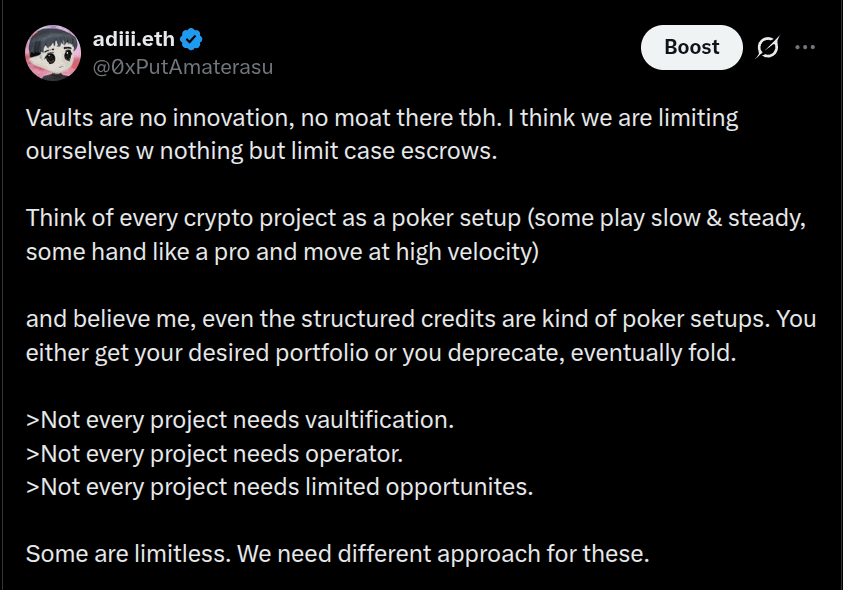
(Below are my personal opinions that come across in midst of designing, developing or bootstrapping some of my own models and research)
This article examines the relationship between vaults and escrows in value-bearing crypto systems. It argues that the vault, as commonly implemented across many protocols, is not a distinct settlement primitive but a constrained form of escrow in which the release condition has been reduced to a single operator-controlled signature while traditional depositor protections, including neutral arbitration and timeout-based recovery, have been removed.
Building on this observation, the article introduces a generalized settlement model based on three parameters: release authority, release condition, and settlement velocity. Within this framework, a wide range of financial systems, including structured credit, can be represented as settlement games that differ only in their parameterization. The analysis further distinguishes between bounded and unbounded opportunity systems and argues that these two categories require fundamentally different settlement architectures. While bounded systems often benefit from custodial coordination, unbounded systems are generally better served by protocol-enforced settlement mechanisms that minimize discretionary authority.
An escrow is a settlement contract that temporarily holds assets until a predefined release condition has been satisfied. Traditional escrow systems share two fundamental properties. First, the entity responsible for releasing funds is expected to remain neutral with respect to the participating parties. Second, if the intended transaction cannot be completed, depositors retain a protocol-defined mechanism for recovering their assets after a specified period.
Vaults retain the custody function of escrow but frequently omit both of these properties. In many production systems, the release condition consists solely of a signature produced by an operator-controlled key. No externally verifiable condition determines whether assets may leave the contract, and users cannot independently satisfy the release condition.
This characterization is observable directly from common implementations. Deposited assets are transferred into the custody of the vault contract itself using instructions equivalent to safeTransferFrom(msg.sender, address(this), amount). Once transferred, the contract becomes the sole custodian of user funds. Expiration mechanisms generally apply only to vouchers or authorizations issued by the operator rather than to idle user balances. Consequently, users who have deposited assets but have not entered an active settlement process often lack a protocol-defined method for reclaiming their funds without operator approval.
Under these conditions, the vault is more accurately described as a constrained form of escrow than as a new settlement primitive. The custody model remains unchanged, but the depositor protections traditionally associated with escrow have been removed. Neutral arbitration is replaced by unilateral authority, and timeout-based recovery is eliminated. The resulting design simplifies operational control while increasing trust assumptions.
The settlement-game model extends beyond crypto-native systems. Traditional financial infrastructure can be described using the same framework, demonstrating that the model captures a broader class of settlement mechanisms rather than a blockchain-specific phenomenon.
Structured credit provides a useful example. In a tranched credit vehicle, investors commit capital to a common pool. Each tranche represents a position with a defined level of risk and priority during distribution. Cash flows generated by the underlying assets are allocated according to a predetermined waterfall, which determines the order and amount of every payout.
Within the settlement-game framework, committed capital corresponds to the settlement pot, tranches represent participant positions, and the waterfall functions as the release mechanism that redistributes value. The settlement process produces a finite set of outcomes. Investors either achieve the expected portfolio performance or experience impairment through default, write-down, or credit deterioration.
The three model parameters remain applicable. Release authority is exercised by the servicer or manager operating within the constraints of the governing agreements. Release conditions are defined by contractual covenants, payment waterfalls, and credit events. Settlement velocity is moderate, reflecting periodic repayments, portfolio rebalancing, and scheduled distributions.
From a structural perspective, a vault and a structured credit vehicle perform the same underlying function. Both receive committed capital, apply predefined settlement rules, and redistribute value according to those rules. Their differences arise from parameter selection rather than from fundamentally different architectures. This observation has broader implications. If two systems from different financial domains can be represented using the same settlement model, then the decision to introduce a vault should be understood as a choice of settlement parameters rather than the introduction of a new primitive. Many protocols adopt custodial vaults as a default architectural pattern without first determining whether their settlement characteristics actually require that level of discretionary control.
Not every settlement game operates under the same economic constraints. The cardinality of available opportunities fundamentally changes the settlement architecture that is appropriate.
A bounded opportunity system is one in which outcomes are finite and inherently scarce. Participants compete for access to a limited pool of value, and the protocol must determine how that value is distributed. Examples include structured credit, auctions, prediction markets, tournaments, insurance pools, and many custodial financial products. In these systems, arbitration is an intrinsic part of settlement because multiple participants compete for mutually exclusive outcomes.
An unbounded opportunity system operates differently. Opportunities are not allocated through scarcity but emerge continuously through permissionless interaction. Value can move directly between participants or against open markets without requiring an intermediary to determine entitlement. Decentralized exchanges, payment channels, state channels, peer-to-peer markets, and many programmable financial protocols fall closer to this category.
The distinction is significant because bounded systems naturally justify stronger coordination mechanisms. When scarce outcomes must be allocated, an operator or protocol-defined authority performs necessary work by resolving conflicts and enforcing distribution rules. The same assumption does not necessarily hold for unbounded systems. Introducing discretionary custody into a system that does not require arbitration increases the trust surface without introducing new settlement capabilities. The additional authority exists only because it has been designed into the architecture rather than because the settlement process depends on it.
This observation leads to a practical design principle. Protocols should select the weakest release authority that satisfies their settlement requirements. If deterministic protocol logic or mutually verifiable state transitions are sufficient to complete settlement, introducing discretionary operator control provides little technical benefit while increasing custodial assumptions.
A vault may still serve a legitimate role within an unbounded system, but only for the bounded portion of its value flow. Funds actively participating in a settlement process may require temporary custody, whereas idle balances or open-ended user funds generally do not. Extending vault custody beyond its necessary scope increases systemic trust requirements without improving settlement correctness.
The practical consequence of this model is straightforward. Rather than defaulting to operator-controlled vaults, protocol designers should minimize discretionary authority wherever the settlement process permits.
Several design alternatives illustrate this progression.
The simplest improvement is timeout-based recovery. If assets remain inactive beyond a predefined period, users regain the ability to withdraw their funds without operator approval. This restores one of the fundamental protections traditionally associated with escrow while leaving the core settlement process unchanged.
A stronger approach is co-signed settlement. Instead of authorizing withdrawals through a unilateral operator signature, settlement requires agreement between all participating parties. Trust becomes limited to the assets actively involved in the current settlement rather than extending across every deposited balance.
The strongest approach replaces discretionary authorization entirely with protocol-enforced settlement. State channels, payment channels, validity proofs, zero-knowledge systems, optimistic dispute mechanisms, and similar constructions bind asset release to verifiable protocol state rather than operator judgment. Under these designs, the settlement authority may temporarily delay execution during disputes, but it cannot unilaterally redirect user funds.
These approaches should not be viewed as competing architectures. They represent different points within the same settlement model. Each changes the release authority and release condition while preserving the underlying objective of securely transferring value. The appropriate design depends on the settlement game's characteristics rather than on convention.
Defaulting to custodial vaults introduces measurable security and operational risks. Because user assets accumulate under a single administrative authority, the vault balance becomes a concentrated target. Compromise of the operator, administrative key, or privileged execution path can affect every participant simultaneously.
These risks may be acceptable in bounded systems where centralized coordination is unavoidable and where operational controls, auditing, and regulatory oversight reduce the likelihood of failure. The same assumptions become more difficult to justify in systems whose settlement process could otherwise operate without discretionary intermediaries. Trust assumptions should also remain internally consistent throughout the protocol. A system that advertises cryptographic correctness for execution, randomness, or state transitions should provide comparable guarantees for custody whenever possible. Verifiable execution combined with discretionary asset release creates an asymmetry in the trust model. Sophisticated participants are likely to evaluate custody separately from execution and assign additional risk where discretionary control remains.
Settlement finality also deserves explicit consideration. Many blockchain systems distinguish between transaction inclusion and irreversible finality. Release conditions that depend on finalized state should treat finality as an explicit prerequisite rather than assuming immediate confirmation. Failure to distinguish between these states can introduce settlement inconsistencies during periods of network congestion, delayed finality, or chain reorganization.
The central argument of this article is that vaults should be understood as one point within a broader design space rather than as the default settlement primitive for value-bearing systems.
Viewed through the settlement-game model, a vault represents a constrained form of escrow in which release authority has become highly centralized and depositor protections have been reduced. Whether this trade-off is appropriate depends entirely on the characteristics of the settlement game being implemented.
The proposed framework evaluates settlement systems using four dimensions: release authority, release condition, settlement velocity, and opportunity cardinality. Together, these parameters provide a systematic method for reasoning about settlement architecture across both crypto-native and traditional financial systems.
The objective is not to eliminate vaults. Vaults remain appropriate wherever bounded settlement requires coordination, arbitration, or controlled distribution of scarce outcomes. The objective is to discourage their indiscriminate application to systems that do not require those properties.
A protocol should not begin with a vault and then justify its existence. It should begin with the settlement requirements of the system and introduce only the minimum level of authority necessary to satisfy them. When settlement can be enforced through protocol rules rather than discretionary control, reducing trust assumptions is generally the more robust design choice.
A useful principle follows from this framework:
Bounded settlement games require dealers. Unbounded settlement games should minimize or eliminate them.
If this principle holds across a broad range of protocols, then vaultification is not a universal design pattern. It is a parameter choice.